

Credit Card payments allow customers to complete transactions using their debit or credit cards through online authorization processed by the acquiring network.
In a one-step payment scenario, the transaction is authorized and captured in a single operation. Once the cardholder successfully completes authentication (when required), the payment is immediately approved and funds are captured without requiring a separate capture request from the merchant.
This model is commonly used when the final transaction amount is known at checkout and immediate confirmation is required.
How It Works
In a typical Credit Card one-step payment flow:
- The merchant initiates a payment request through the SIBS Payment Gateway.
- The customer provides card details through a secure payment form or hosted page.
- The transaction is sent to the acquiring network for authorization.
- Strong Customer Authentication (e.g., 3D Secure) is applied when required.
- Upon successful authorization, the payment is immediately captured.
- The final transaction result is returned to the merchant system.
The entire flow occurs in real time and typically completes within seconds.
Although Credit Card transactions are typically completed in real time, merchants should still implement webhook processing and, where needed, Status Inquiry mechanisms to support reliable transaction lifecycle monitoring, operational reconciliation, and transaction status follow-up.
The SPG transactionID should be treated as the authoritative identifier for transaction monitoring, webhook correlation, reconciliation, refund operations, and Status Inquiry requests throughout the transaction lifecycle.
Workflow Characteristics
The Credit Card one-step flow has the following characteristics:
- Real-time authorization
- Immediate capture
- Strong Customer Authentication when required
- Synchronous response
- Immediate transaction outcome
- Possible authentication or authorization declines
There is no separate settlement step initiated by the merchant. Once authorized, the funds are considered captured and will be settled according to the merchant’s agreement with the acquiring partner.
Transaction Lifecycle
The following diagram illustrates the operational lifecycle of a Credit Card one-off payment within the SIBS Payment Gateway, including customer authentication, authorization processing, transaction completion, and merchant reconciliation.
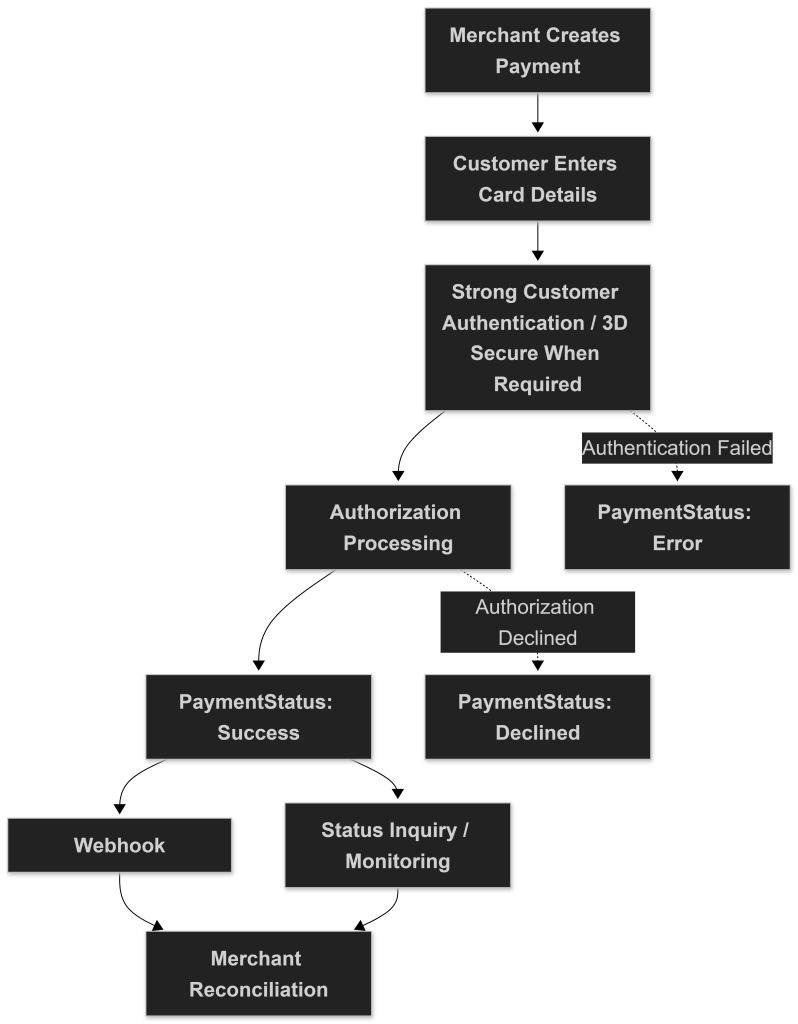
The lifecycle of a Credit Card one-step payment typically includes:
- Payment creation
- Customer authentication (when required)
- Authorization processing
- Successfully authorized and captured
- Authentication failed
- Authorization declined
If authentication fails or authorization is declined, the transaction is not completed.
Use Cases
Credit Card one-step payments are commonly used in:
- Standard e-commerce checkout flows
- Digital goods and services
- Subscription sign-ups with immediate activation
- Retail and omnichannel payments
- Low-friction, real-time purchase environments
This payment method is particularly suited for environments where:
- Immediate confirmation is required
- The final transaction amount is known at checkout
- Customers expect a fast and familiar payment experience
For transaction lifecycle monitoring and final transaction state validation, refer to E.2 – Status Inquiry / Get Status.
For webhook delivery and asynchronous transaction notifications, refer to E.1 – Webhooks (Notifications).
Practical implementation examples, Postman collections, Credit Card payment scenarios, and integration examples are documented in F. Technical Examples and Best Practices.
The Sandbox Payment Simulator may also be used to validate Credit Card payment flows, customer authentication behaviour, transaction lifecycle progression, and operational request/response payloads in the sandbox environment.
Example sandbox simulator entry point
Particularities in the SIBS Context
When working with Credit Card one-off payments in SIBS SPG, several platform-specific aspects should be considered:
- Strong Customer Authentication (3D Secure) may be required depending on issuer and regulatory requirements
- Authentication and authorization outcomes should always be validated through transaction status monitoring mechanisms
- Webhook notifications and, where needed, Status Inquiry should be implemented for reliable transaction lifecycle monitoring and reconciliation
- Temporary processing states may occur before final transaction confirmation
- Proper transaction monitoring is important to guarantee operational consistency and accurate reconciliation
Integration Context
Within the SIBS Payment Gateway, Credit Card payments support both one-step and two-step models. In the one-step model, authorization and capture occur within the same transaction request.
The following sections describe the technical integration flow, authentication handling, and post-payment operations for credit card payments.